
EngadgetGeneral Tech
Meta will alert parents if their teens discuss self harm
Meta has rolled out a new safeguard for teens' AI interactions.
Read source article
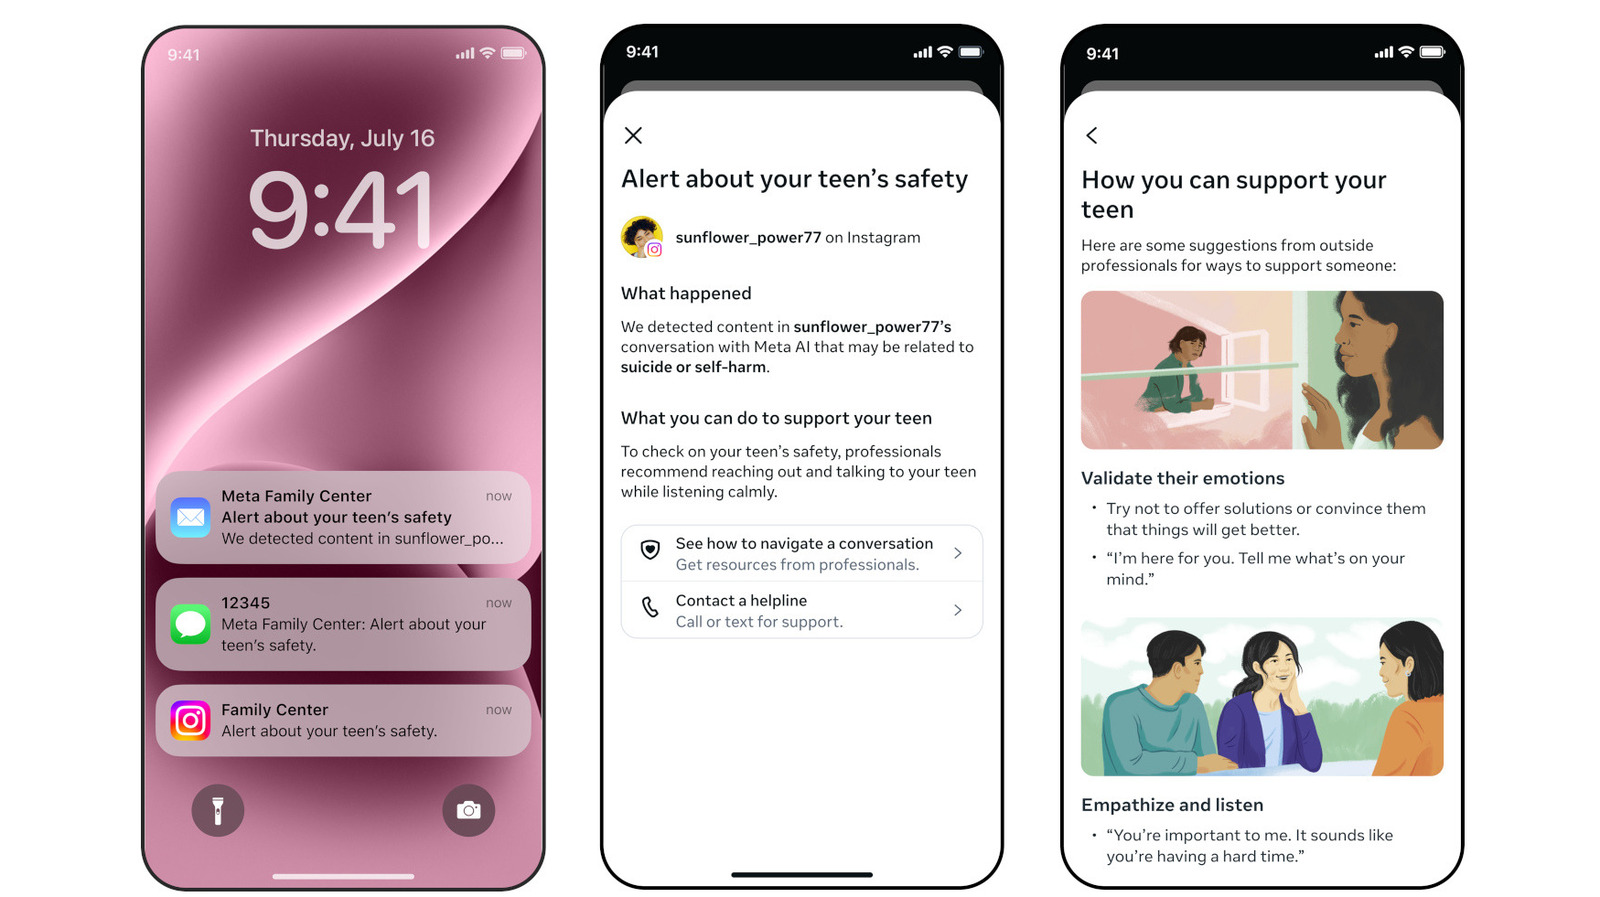
Meta has rolled out a new safeguard for teens' AI interactions.
The updates come as Meta and other tech companies are facing scrutiny from regulators and parents around how AI chatbots respond to users in crisis, particularly teenagers.
AI-and-X subsidiary now claims to offer ‘complete user privacy’ days after Elon Musk confirmed the data would be deleted
<blockquote> <p><em>Install guide and config at <a href="https://www.curatedmcp.com/install/twilio-mcp/claude-desktop" rel="noopener noreferrer">curatedmcp.com</a></em></p> </blockquote> <h1> Twilio MCP: Control SMS, Voice, and Chat from Your AI Workflows </h1> <p>The official Twilio MCP server bridges the gap between AI agents and real-world communications. Instead of manually calling Twilio APIs, you can now ask Claude, Cursor, or Windsurf to send SMS notifications, trigger voice calls, or man
Storm sends winds whipping beyond cloud giant, knocking out services including Hugging Face and the UK's National Lottery
Article URL: https://medium.com/airbnb-engineering/from-weeks-to-a-day-how-we-made-llm-evaluation-fast-enough-to-iterate-on-14e2d35198b4 Comments URL: https://news.ycombinator.com/item?id=48932815 Points: 2 # Comments: 1
<pre style='white-space:pre-wrap;width:81ex'>fix(ui): honor UTC in usage session detail timelines (#108579) * fix(ui): honor timezone in usage detail timeline Apply the selected local or UTC calendar boundaries to session detail points and keep the full final day. Co-Authored-By: OpenAI Codex <noreply@openai.com> * test(ui): make usage timezone regression deterministic Model a non-UTC local calendar through Date getters instead of relying on runtime TZ mutation. Co-Authored-By: OpenAI Codex <nor
Don't need Gemini in Gmail? There's a way to disable it. Here's a step-by-step guide.

<pre style='white-space:pre-wrap;width:81ex'>fix(anthropic-vertex): keep ADC fetch provider-local (#108350) * fix(anthropic-vertex): shim native fetch so Google auth avoids gaxios's node-fetch import @anthropic-ai/vertex-sdk's bundled gaxios only uses native fetch when a global `window.fetch` exists; otherwise it dynamically imports `node-fetch`, which can fail to resolve depending on how the plugin's dependencies are installed. That failure surfaces deep inside gaxios's token-exchange path as "
<pre style='white-space:pre-wrap;width:81ex'>fix(gateway): agent model overrides cannot be cleared (#108734) * fix(gateway): allow clearing agent model overrides * fix(protocol): preserve Swift agent model compatibility * fix(protocol): preserve null when Swift decodes agent updates --------- Co-authored-by: Peter Steinberger <steipete@gmail.com></pre>
Google Cloud has partnered with Parallel Web Systems to natively integrate Parallel's search infrastructure as a web grounding provider on the Gemini Enterprise Agent Platform. This integration enables developers to anchor their AI agents in verifiable, real-time web results, significantly improving factual accuracy for complex enterprise workflows. Additionally, the partnership offers expanded architectural flexibility, allowing users to programmatically extract, permanently cache, and process
<pre style='white-space:pre-wrap;width:81ex'>fix(line): run post-ack webhook processing on its own admitted work root (#107734) * fix(line): run post-ack webhook processing on its own admitted work root LINE acks the webhook and dispatches event processing fire-and-forget on the same async chain. The HTTP request admission that chain inherited is released as soon as the route handler returns, and a released admission refuses subordinate queue work - so every LINE inbound agent turn fails with "G
<p>Two coding-agent tasks start from commit <code>A</code>. Task X edits authentication. Task Y edits logging. While both run, a human pushes commit <code>B</code>.</p> <p>If the patches do not identify their base, “apply both” is unsafe. Parallel agent sessions are a consistency problem, not only a speed feature.</p> <p>Here is a black-box experiment for <a href="https://monkeycode-ai.net/" rel="noopener noreferrer">MonkeyCode SaaS</a>, not a claim about its concurrency implementation.</p> <h2>
<p>Every time I submit a Pull Request (PR) to an open-source project, I watch the CI pipeline kick off. More and more often, an AI assistant like CodeRabbit, Copilot, or Claude pops up a few minutes later to review my changes, categorize bugs, or suggest updates.</p> <p>It got me wondering: <strong>How hard is it to build one of these from scratch?</strong></p> <p>As it turns out, you don't need a heavy, expensive third-party platform. You can build a fully customized, line-by-line AI code revie
<p>An agent shows a green “ready” state. The reviewer sees a polished summary, but not the original requirement, target environment, unresolved warnings, or evidence behind the recommendation.</p> <p>Approval is available and practically uninformed.</p> <p>Security review inside AI apps is a current design hotspot. Here is a human-review framework to evaluate in <a href="https://monkeycode-ai.net/" rel="noopener noreferrer">MonkeyCode SaaS</a>. It is not a claim about MonkeyCode's current review
<p>An agent session stops updating at 14:07. Did the model stall, the browser stream disconnect, the managed environment fail, or the task finish while the client missed the final event?</p> <p>Without session-level evidence, those incidents look identical.</p> <p>Here is an OpenTelemetry-inspired acceptance protocol for <a href="https://monkeycode-ai.net/" rel="noopener noreferrer">MonkeyCode SaaS</a>. It does not claim that MonkeyCode exports OpenTelemetry data.</p> <h2> Define one traceable t
<p>Three agent tasks are running. One completes, one needs input, and one fails. If the interface communicates that only through color, reordered cards, or transient toasts, keyboard and screen-reader users can lose the task they were reviewing.</p> <p>Parallel agent-session interfaces are a current developer-tool hotspot. Here is an accessibility audit for <a href="https://monkeycode-ai.net/" rel="noopener noreferrer">MonkeyCode SaaS</a>, not a claim that its current UI has a defect.</p> <h2> M
<p>If an AI coding pilot completes 80 tasks but only 20 survive review, its cost is not “spend divided by 80.”</p> <p>The useful unit is an <strong>accepted engineering task</strong>: bounded work that passes normal checks, receives human approval, and creates no unresolved rollback or security exception.</p> <p>Current discussion about managing AI investment in the agentic era makes explicit exposure limits more important, not less. Here is a vendor-neutral pilot model you can apply to <a href=
<p>A browser-first coding agent removes the usual opening chores: installing runtimes, repairing PATH, authenticating a CLI, and discovering that the “quick test” needs three local services.</p> <p>That convenience creates another risk: starting takes five minutes, while leaving takes five days.</p> <p>Here is a 30-minute exit test for <a href="https://monkeycode-ai.net/" rel="noopener noreferrer">MonkeyCode SaaS</a>. It is a proposed protocol, not a report of measured performance.</p> <h2> Use
Artificial intelligence (AI) is changing offensive security, but it has not changed the standard that matters most: a finding has to be proven before it becomes useful. AI-assisted tools can read code quickly, generate payloads, summarize attack surfaces, explain unfamiliar APIs, and run repetitive testing workflows at impressive speed. That is a real advantage for security teams. It also

Hello everyone I am an astronomy and astrophotography enthusiast. Lately I've had a weird obsession with observatories (like the Vera Rubin or the Extremely Large Telescope). However, I couldn't find a website that has all of them in a map or a comprehensive list. So it was the perfect opportunity to use my unused Fable 5 tokens. The list of the observatories I gathered using ChatGPT Deep Research with GPT 5.6 - Sol. As for the manual work, I will start gathering images for each observatory to u
<p> Control work with your voice. The Siri for work. </p> <p> <a href="https://www.producthunt.com/products/routine?utm_campaign=producthunt-atom-posts-feed&utm_medium=rss-feed&utm_source=producthunt-atom-posts-feed">Discussion</a> | <a href="https://www.producthunt.com/r/p/1198043?app_id=339">Link</a> </p>
Struggling to get traction on LinkedIn despite posting consistently? Wondering what separates content that stops the scroll from posts that actually get shared? In this article, you'll discover a three-part framework for writing LinkedIn posts that capture attention, hold readers through to the end, and drive meaningful shares. Making the LinkedIn Content Gap Work for […] The post Writing Winning LinkedIn Content, Without AI appeared first on Social Media Examiner .
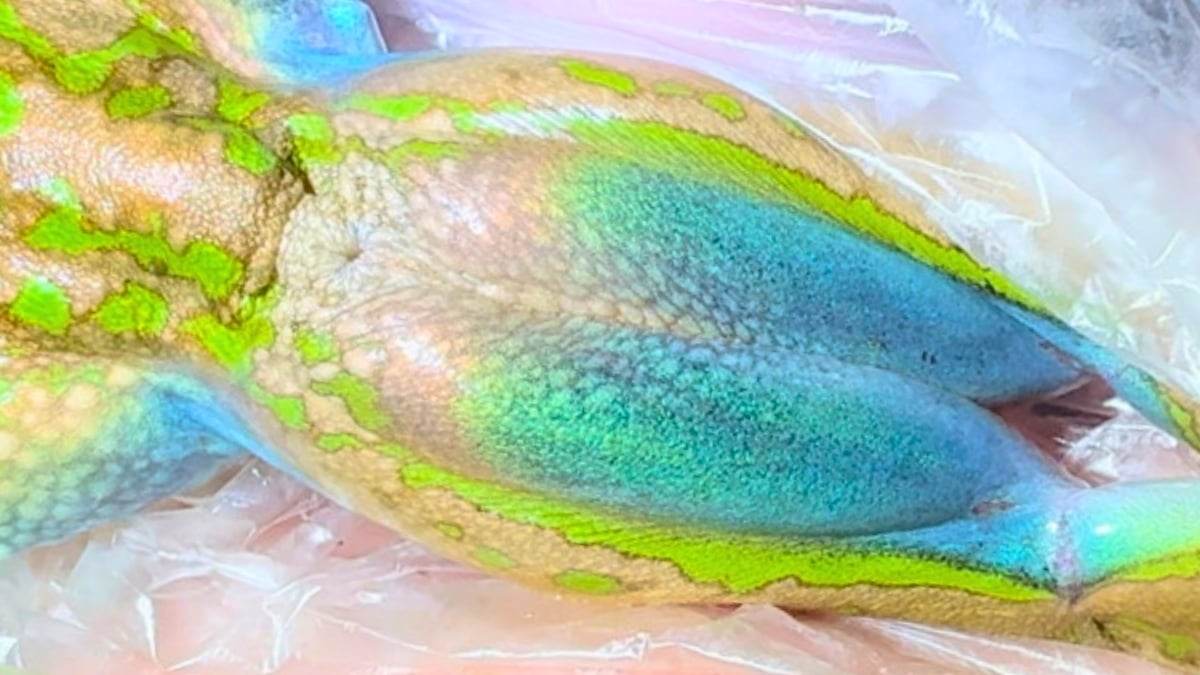
You think you know a guy... ScienceAlert stories are written, fact-checked, and edited by humans, never generated by AI. Don't miss a story, subscribe here.
I’m sick of “opt-out” toggles for automatically enabled generative AI features. It’s past time to make “opt in” the default setting for sensitive features.

From Kylie Jenner Meta glasses to smart beauty mirrors, AI companies are using fashion, influencers, and celebrity culture to reach women.

The group is trying to extend its influence beyond Meta.
Arcrawls can use Gemini Nano + DistilBERT locally to understand page sentiment and even give you daily summaries of your browsing habits — all without sending anything to the cloud. Comments URL: https://news.ycombinator.com/item?id=48932411 Points: 1 # Comments: 0
Thinking Machines Lab, founded by former OpenAI CTO Mira Murati, has released Inkling, a multimodal open-weights model with 975 billion parameters. It leads U.S. open-weights models on the Artificial Analysis Intelligence Index, though top Chinese open models still beat it on some tasks. Pricing starts at $1.87 per million input tokens, and Thinking Machines is pitching Inkling as a base for fine-tuning rather than the most powerful model available. The article Ex-OpenAI CTO Murati's Thinking Ma
Find the best robot pool cleaner deal. Save 29% on the Aiper Scuba S1 at Amazon.

Google DeepMind and Isomorphic Labs are sharing our joint approach to bioresilience and AI models.
<p> Instant, hardware Isolated Sandboxes for AI agents </p> <p> <a href="https://www.producthunt.com/products/createos-sandbox?utm_campaign=producthunt-atom-posts-feed&utm_medium=rss-feed&utm_source=producthunt-atom-posts-feed">Discussion</a> | <a href="https://www.producthunt.com/r/p/1198012?app_id=339">Link</a> </p>
Pull the certificate off the flash of a Shark RV2320EDUS robot vacuum, and you can run root commands on other people's Shark vacuums across the same AWS region: watch the camera, drive the robot, read the map of the house, and take the Wi-Fi password in plaintext. A researcher publishing under the handle tokay0 put the method online on Monday, having tested it only against vacuums he

Roborock’s RockMow X120H robot lawn mower is now available with a $700 launch discount. It uses LiDAR, AI obstacle avoidance, and 4WD for smarter mowing.

Google shipped an update to its open AI model Gemma 4 that speeds up performance on Nvidia Hopper GPUs, fixes tool calling bugs, and addresses problems with truncated responses. The article Gemma 4 gets a stealth update that fixes tool calling bugs and truncated responses under the same name appeared first on The Decoder .
We built LHIC (Local Human Intent Controller) because we were frustrated by existing LLM-based browser agents. Tools like WebVoyager or ServiceNow's baseline agents are amazing, but they are: 1. Slow: Taking 20 to 40 seconds per simple form-fill step. 2. Expensive: Calling GPT or Claude for every single click. 3. Brittle: Failing the second a minor DOM class name shifts. LHIC introduces a "Fast Path / Slow Path" dual-route execution architecture: - Fast Path (Local, 0 LLM call): For standard web
Neko Health has raised $700 million to expand its AI body scans in the United States, starting with a clinic in New York. The company’s preventive screening service combines medical imaging, blood tests, proprietary sensors, and clinician review. The Series C round was led by Lightspeed Venture Partners and co-led by O.G. Venture Partners. Existing […] The post Neko Health raises $700 million to expand AI body scans in the US appeared first on AI News .

Hi, I don't have a long history as OSS builder but I'm now focusing on a project which is keeping me busy and I want to maintain it in the long term. The problem I'm facing is that I have the OSS part (code, public docs, etc) but also some private assets (private docs primarily, my personal notes, AI iterations, etc) which I don't want to push publicly. At the same time I don't want to keep the private stuff local only as they are valuable assets and they might get lost, so gitignore is not a so
OpenAI has disclosed details of GPT-Red, an internal automated red-teaming model that scales prompt injection vulnerability discovery with an aim to fix issues before the tools are deployed widely. "GPT‑Red is a strong red-teamer, and our previous models are highly vulnerable to its prompt injection attacks," the artificial intelligence (AI) company said. "We use GPT‑Red to adversarially train

Article URL: https://www.ted.com/talks/peter_steinberger_how_i_created_openclaw_the_breakthrough_ai_agent Comments URL: https://news.ycombinator.com/item?id=48931821 Points: 1 # Comments: 1